
The SOAR Is Dead. Long Live the AI SOC: A Buyer’s Guide
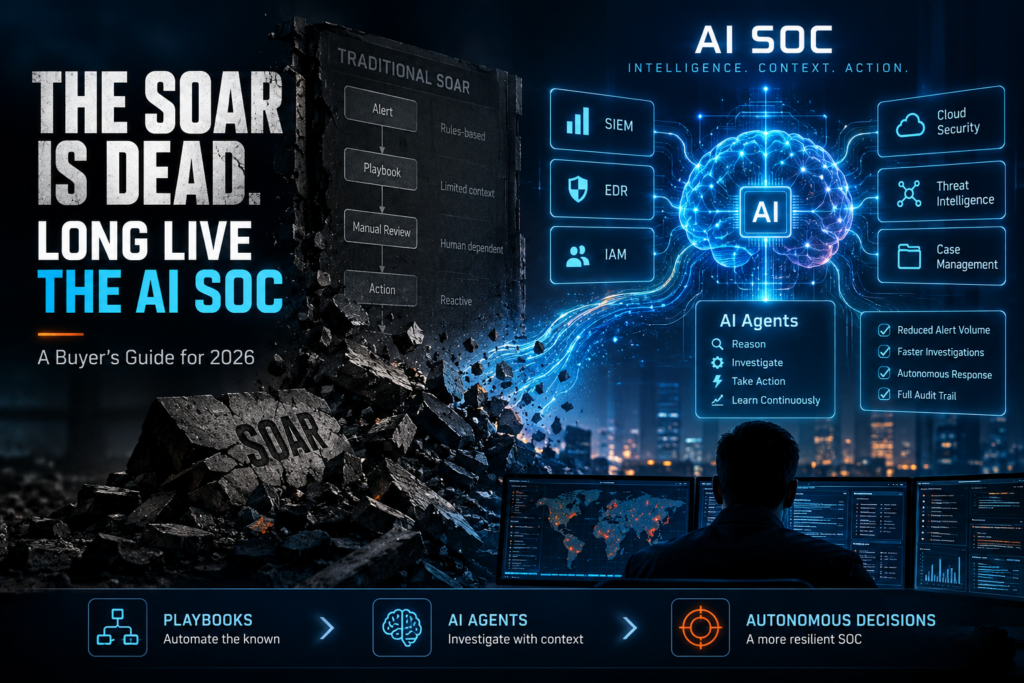
SOAR is not dead. But the category is being absorbed into something larger. Here is how to evaluate what comes next. Every analyst report in 2025-2026 has declared SOAR dead, dying, or evolving. Gartner folded it into SecOps platforms. Vendors rebranded overnight: yesterday’s SOAR is today’s AI SOC, Autonomous SOC, or Agentic Security Platform. The […]
Your AI Vendor Sends Case Data to OpenAI. Does Your Regulator Know?
Most AI-powered security tools route your alert data through third-party LLMs. In regulated markets, that is a compliance problem hiding in your architecture. Your SOAR vendor added an AI assistant last year. It summarizes cases, recommends response actions, and generates investigation narratives. Your analysts love it. Your compliance team has not asked where the AI […]
Automated Incident Response — What It Actually Means in 2026
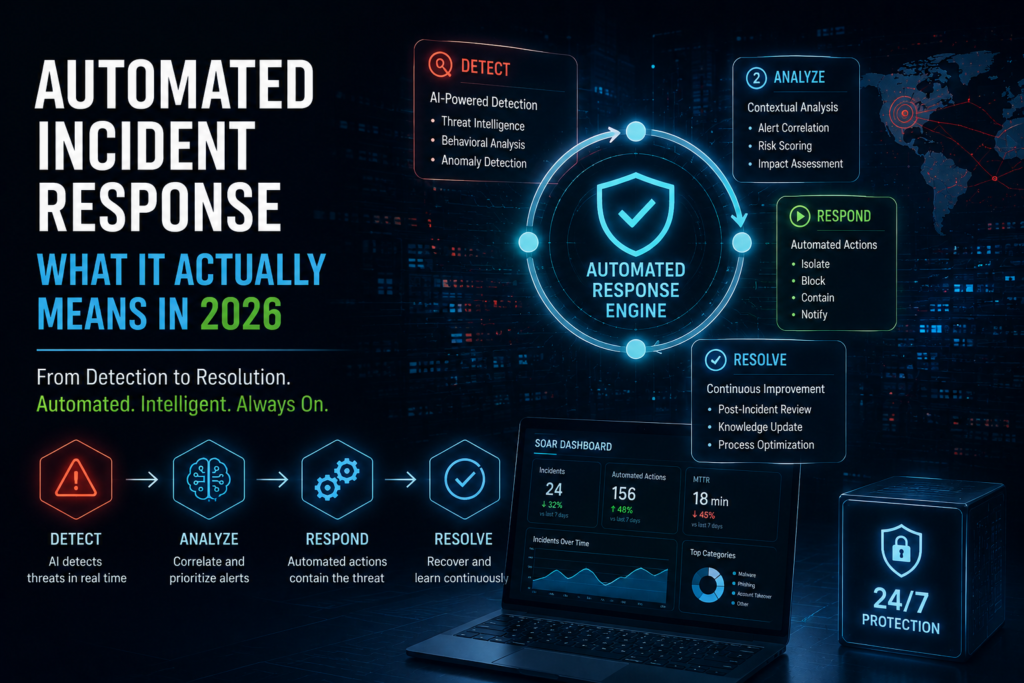
The industry has been promising automated response for a decade. Here is what it looks like when it actually works, what it looks like when it doesn’t, and where the line should be. Securaa | July 2026 | 5 min read In 2020, automated incident response meant a SOAR playbook that enriched an IP address […]
The Board Is Going to Ask How Your AI Made That Decision.
What Will You Say? You have about 18 months before this question lands in a board meeting. Here is how to have an answer ready. Boards have learned to ask about cybersecurity. After a decade of headline breaches, most directors can ask competent questions about incident response plans, backup strategies, and third-party risk. They learned […]
How Securaa investigated a phishing alert in 47 seconds

At 10:42 on a Wednesday morning, an employee in accounts payable forwarded an email to the security inbox with a one-line note. This looks off. The email claimed to be from the company’s bank, warned of a hold on an outgoing wire, and asked her to confirm account details through a link. She didn’t click […]
On-prem AI agents: same intelligence, zero cloud dependency

There’s a conversation that plays out in a lot of security teams the moment AI comes up. Someone has seen a demo of an AI agent that triages alerts, writes up cases, and clears the queue overnight. They want it. Then the question gets asked that ends the excitement in about four seconds. Where does […]
Insider threat investigation: building the identity chain from alert to verdict

An alert comes in on a Thursday afternoon. A sales account manager downloaded the regional customer list, about 400 records, to her laptop. The alert is low severity. Employees pull customer lists all the time. She has legitimate access. Nothing about the download itself looks wrong. Two weeks later, HR flags that she resigned. Her […]
Black-Box AI in the SOC Is Professionally Negligent
If your AI agent makes decisions your analysts cannot explain, you do not have automation. You have liability. A SOC analyst closes a case. The AI agent told them it was a false positive. They click confirm and move on. They do not know why the agent reached that verdict. The agent does not tell […]
The Detection Engineering Feedback Loop:

How Your SOC Gets Smarter Every Day Good detections are not written once. They are grown through a continuous cycle of measurement, failure analysis, and refinement that most SOCs never formalize. Every SOC has that one Sigma rule someone wrote 18 months ago. It fires 300 times a day. Nobody remembers why. Analysts auto-close the […]
How to Measure Your AI Agents’ Performance

(The Metrics That Actually Matter) Most teams track the wrong numbers. Here is what separates useful AI agent metrics from expensive vanity dashboards. You deployed AI agents in your SOC. The vendor told you they would reduce alert fatigue, accelerate investigations, and free your analysts to focus on real threats. Six months in, your CISO […]
